
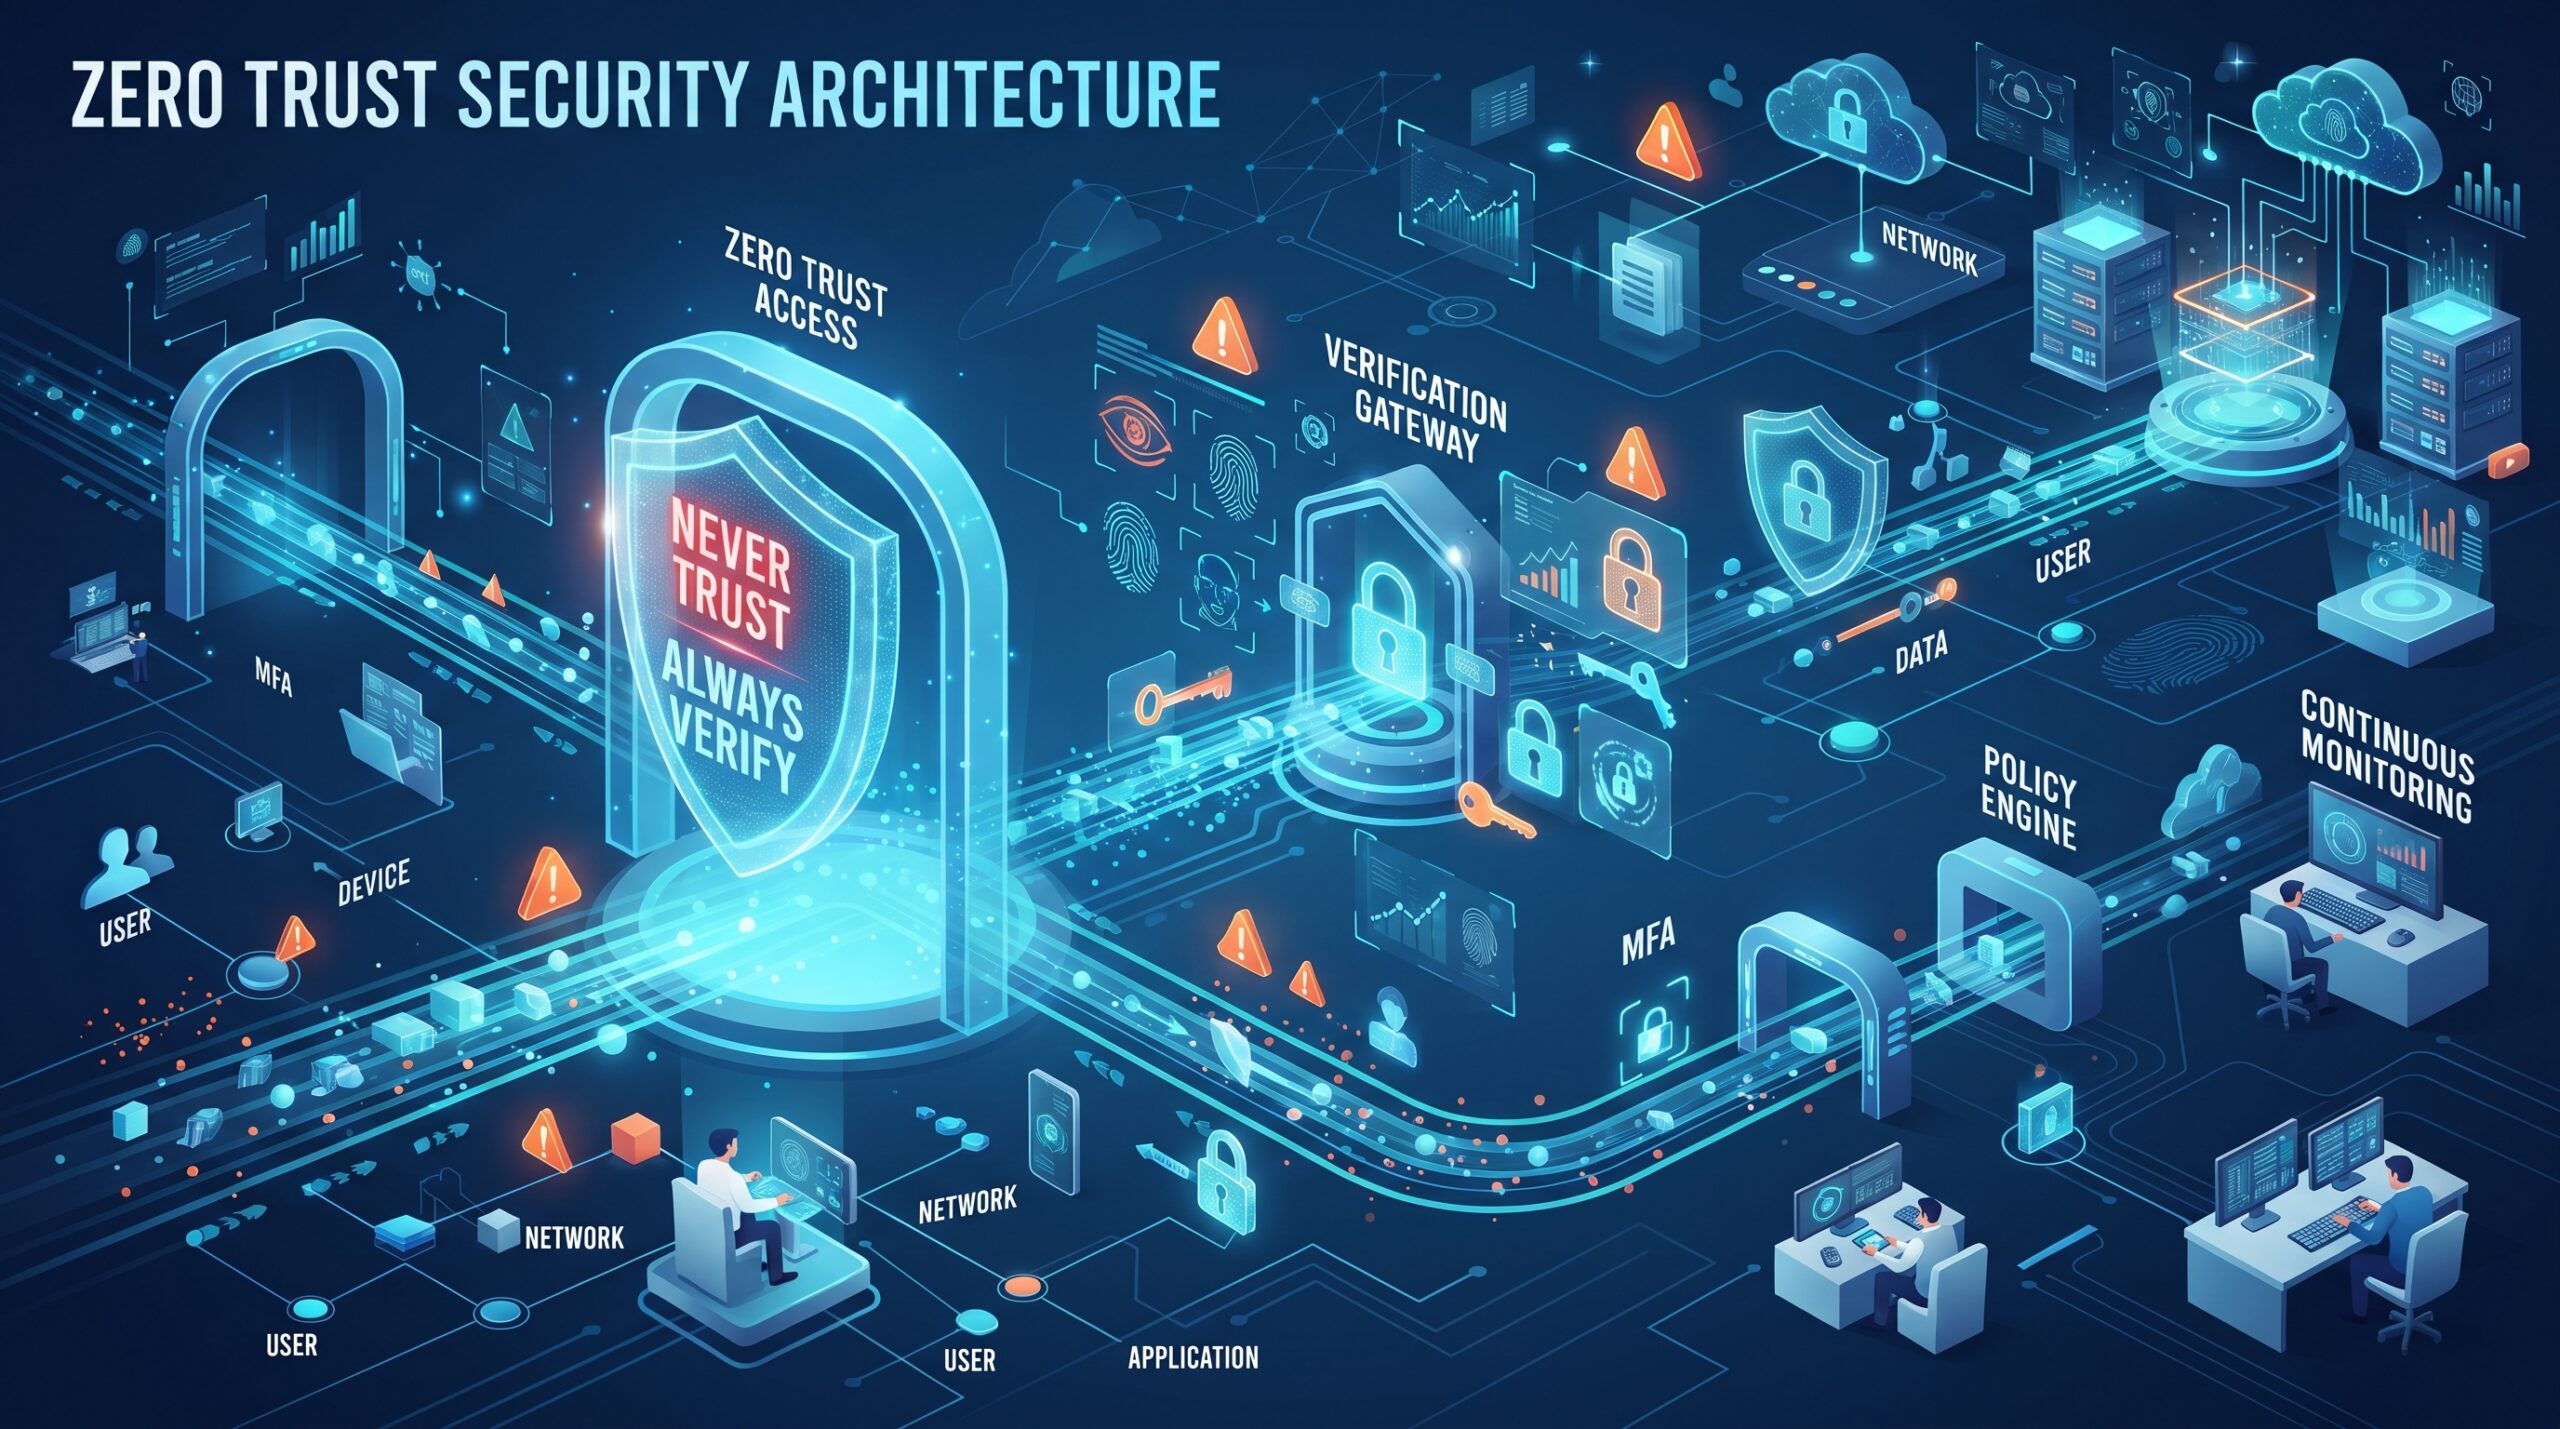
For decades, corporate network security operated on a castle-and-moat model: build strong defenses at the perimeter, and once a user or device is inside, trust it implicitly. That model has collapsed under the weight of cloud computing, remote work, and increasingly sophisticated attackers who have learned to exploit exactly this kind of implicit trust. Zero trust architecture represents a fundamental rethinking of network security, built on a simple but powerful principle: never trust, always verify. This article explores what zero trust actually means in practice, why businesses are rapidly adopting it, and how organizations can begin implementing it.
The Problem With Perimeter-Based Security
Traditional network security assumed that threats primarily came from outside the organization. Firewalls, VPNs, and intrusion detection systems were designed to keep attackers out, while anyone who successfully authenticated at the perimeter — an employee logging into the VPN, for instance — was generally trusted to move freely within the internal network.
This approach has two critical weaknesses. First, once an attacker breaches the perimeter, whether through phishing, stolen credentials, or an exploited vulnerability, they often face little additional resistance moving laterally through the network to reach sensitive systems. Second, the perimeter itself has become increasingly difficult to define. With employees working from home, contractors accessing systems remotely, and critical applications hosted across multiple cloud providers, there is no longer a single, well-defined boundary to defend.
What Zero Trust Actually Means
Zero trust is not a single product or technology; it’s a security philosophy and architectural approach built around several core principles:
Verify explicitly. Every access request is authenticated and authorized based on all available data points, including user identity, device health, location, and the sensitivity of the resource being accessed — regardless of whether the request originates inside or outside the traditional network perimeter.
Use least-privilege access. Users and systems are granted only the minimum level of access necessary to perform their function, limiting the potential damage from a compromised account.
Assume breach. Rather than assuming the network is secure until proven otherwise, zero trust architectures operate under the assumption that an attacker may already be present, and design controls to limit lateral movement and detect anomalous behavior quickly.
Core Components of a Zero Trust Architecture
Identity and Access Management (IAM)
Strong identity verification is the foundation of zero trust. This typically includes multi-factor authentication (MFA), which requires users to verify their identity through multiple methods beyond just a password, and often extends to risk-based authentication that adjusts verification requirements based on contextual signals like unusual login locations or times.
Micro-Segmentation
Rather than treating the internal network as a single trusted zone, micro-segmentation divides it into small, isolated segments, each with its own access controls. This means that even if an attacker compromises one segment, they cannot automatically move to others without passing through additional verification.
Device Health Verification
Zero trust architectures typically evaluate the security posture of a device before granting access — checking factors such as whether the operating system is up to date, whether endpoint security software is active, and whether the device shows signs of compromise.
Continuous Monitoring and Analytics
Rather than a one-time authentication check, zero trust systems continuously monitor user and device behavior throughout a session, watching for anomalies that might indicate a compromised account or insider threat, and can trigger re-authentication or session termination when suspicious activity is detected.
Software-Defined Perimeters
Instead of relying on traditional VPNs that grant broad network access once connected, zero trust network access (ZTNA) solutions create secure, encrypted connections to specific applications only, without exposing the broader network.
Why Businesses Are Adopting Zero Trust
Remote and hybrid work have made perimeter security obsolete. With employees connecting from home networks, coffee shops, and shared workspaces, there is no consistent physical boundary to secure.
Cloud adoption has distributed critical assets. Applications and data that once lived entirely within a corporate data center are now spread across multiple cloud providers and SaaS platforms, each with its own access model.
Insider threats and credential theft remain leading attack vectors. Because zero trust does not grant implicit trust based on network location, it significantly reduces the damage a compromised credential or malicious insider can cause.
Regulatory pressure is increasing. Government agencies and regulated industries are increasingly mandating zero trust principles as part of compliance frameworks, pushing broader adoption across supply chains.
Implementation Challenges
Adopting zero trust is a significant undertaking, and organizations commonly encounter several challenges:
Legacy infrastructure compatibility. Older applications and systems were often not designed with granular access controls in mind, and may require additional investment or workarounds to integrate into a zero trust model.
Organizational complexity. Zero trust requires close coordination between IT, security, and business units to correctly define access policies without disrupting legitimate workflows.
User experience trade-offs. Overly aggressive verification requirements can frustrate users and reduce productivity, so organizations need to carefully balance security with usability.
Cultural resistance. Shifting from an implicit trust model to continuous verification represents a significant change in how employees and IT teams think about network access, and can face internal resistance without clear communication about the reasoning behind it.
A Practical Roadmap for Getting Started
Most successful zero trust implementations follow a phased approach rather than attempting a complete architectural overhaul at once:
- Inventory and classify assets. Identify what data, applications, and systems exist, and classify them by sensitivity to prioritize protection efforts.
- Strengthen identity verification first. Implementing MFA across all accounts is often the highest-impact, lowest-disruption first step.
- Map data flows and access patterns. Understand how users, devices, and applications currently interact to design appropriate segmentation and policies.
- Implement least-privilege access incrementally. Start with the most sensitive systems and expand gradually rather than attempting to reconfigure access for the entire organization simultaneously.
- Deploy continuous monitoring. Build visibility into user and device behavior to detect anomalies and refine policies over time.
- Iterate based on real-world usage. Zero trust is not a one-time project; policies should be continuously refined based on observed behavior and emerging threats.
Measuring Zero Trust Maturity
Organizations can assess their zero trust progress across several dimensions, including identity verification strength, device trust evaluation, network segmentation granularity, application access controls, and data protection measures. Several published maturity models offer structured frameworks for benchmarking progress and identifying the highest-priority next steps.
The Business Case Beyond Security
While risk reduction is the primary driver, zero trust architecture can also deliver operational benefits. Simplified remote access models can improve employee experience compared to traditional VPN connections. Granular visibility into access patterns can support more informed business decisions about resource allocation and application usage. And a well-implemented zero trust model can actually reduce long-term IT complexity by replacing a patchwork of legacy security tools with a more coherent, unified approach.
Conclusion
Zero trust architecture represents a necessary evolution in how organizations think about security in a world without clear network boundaries. While implementation requires significant planning and investment, the core principle — verifying every access request based on identity, device health, and context rather than assuming trust based on network location — addresses the fundamental weaknesses of traditional perimeter security. Organizations that approach zero trust as a phased, ongoing journey rather than a single project are best positioned to build resilient, adaptable security postures for the years ahead.